ShinyHunters claims FBI breach via PeopleSoft
The extortion group ShinyHunters says it used an unpatched Oracle PeopleSoft zero-day to reach FBI systems and take data on agents and job applicants, and the FBI is investigating.
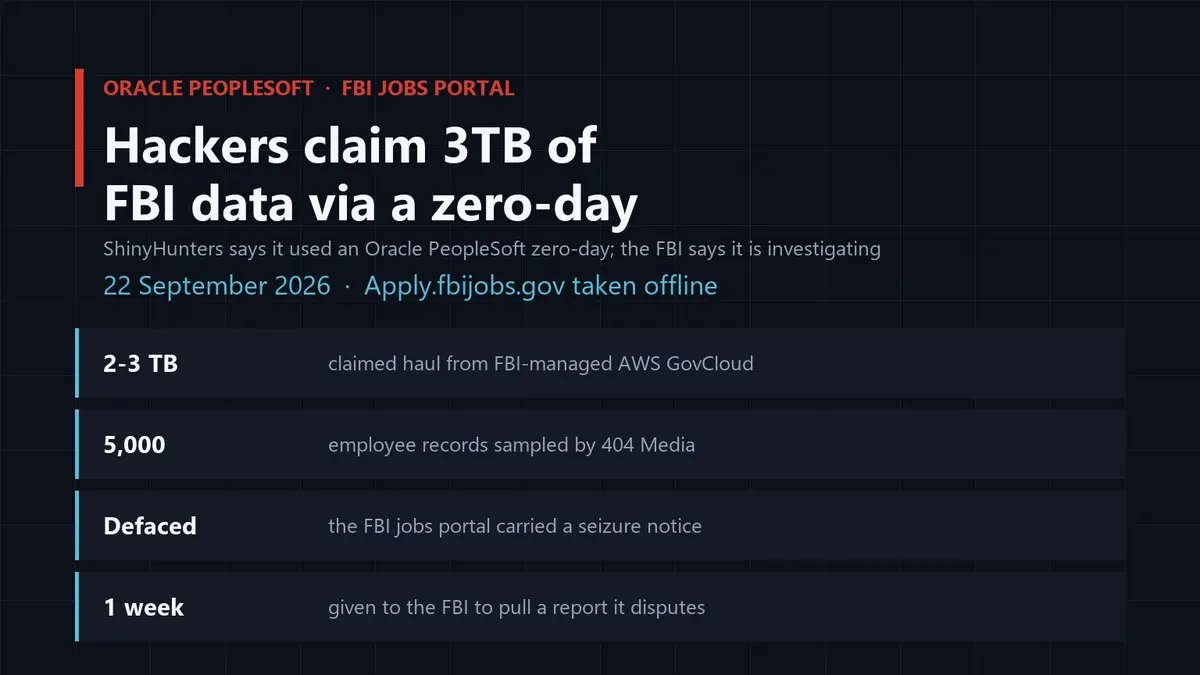
A hacking group best known for large-scale data theft and extortion says it has broken into FBI systems, taken data on current and former agents and job applicants, and defaced the bureau’s recruitment portal. ShinyHunters made the claim on its dark-web leak site on Tuesday, and an FBI spokesperson told 404 Media the bureau is aware of the claims about unauthorised activity affecting FBIjobs.gov and is investigating.
What the group says it did
The group told BleepingComputer it used a previously unknown remote code execution flaw in Oracle PeopleSoft, an HR and recruitment platform, on Monday night, then moved laterally into FBI-managed infrastructure on AWS GovCloud and pulled between two and three terabytes of data. It says the haul covers current and former employees, job applicants and internal services it names as Criminal Justice, HR and Medlink, and it claims the same flaw is being worked against other organisations. Access to the jobs portal, apply.fbijobs.gov, is currently unavailable and carried a notice claiming the site had been seized by the group before a maintenance message replaced it.
What has actually been verified
404 Media received a sample said to hold about 5,000 FBI employee records and found that some of the phone numbers matched people with the same names, including numbers associated with Department of Justice personnel. That is strong evidence of real data in the sample, and it is not proof of the scale the group claims. BleepingComputer says plainly that it has not independently verified the zero-day, the lateral movement or the volume, and Oracle has published no advisory for it. Treat the terabytes, the service list and the reach of the flaw as the group’s account of its own work.
Why it matters
The data described is the raw material of counterintelligence: names, home addresses, phone numbers and family details that can be used to pressure people with access to investigations. TechCrunch notes this is the second known intrusion touching FBI systems this year, after hackers reached a system used for wiretap and foreign-intelligence warrants, and the bureau’s director had a personal email account leaked by an Iran-linked group. ShinyHunters says the operation is not financially motivated and is demanding that the FBI withdraw a report it describes as containing false allegations about the group, giving the bureau a week.
Our opinion
The most revealing line in this story is the group’s own: asked whether it was about to extort the FBI, its representative said what it plans is not something they would call extortion, maybe coercion. Motive is the whole story here. ShinyHunters is not selling anything it expects a government to buy; it is trying to get a warning about its methods taken down, which makes the publicity the point and gives every outlet running the claim a role in the operation whether it wants one or not. That is an argument for precision rather than for silence. Reporting what the FBI has said, what reporters have checked against public records, and what remains the group’s word is the honest shape of the story, and it is also the only version that ages well if the volume turns out to be three terabytes or thirty megabytes.